
By Neelesh Pateriya, Barry Yuan
Publication Date: 2026-10-23 16:10:00
In March, we wrote that Learning Labs would add GPU-backed environments so learners could run Cisco’s own AI models hands-on. The first two of those labs are now live, built on Antares. This post covers the labs first, then goes behind the scenes on how the platform runs GPU workloads. If you’re here for the security labs, the first half is all you need.
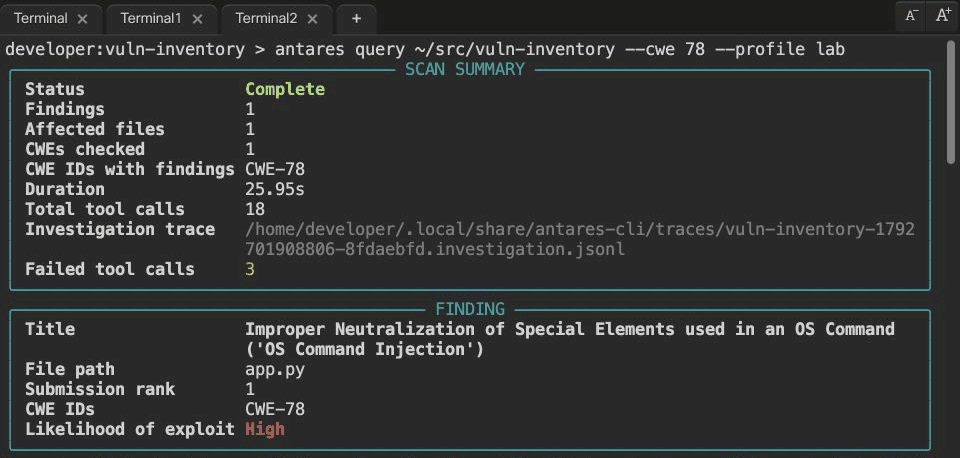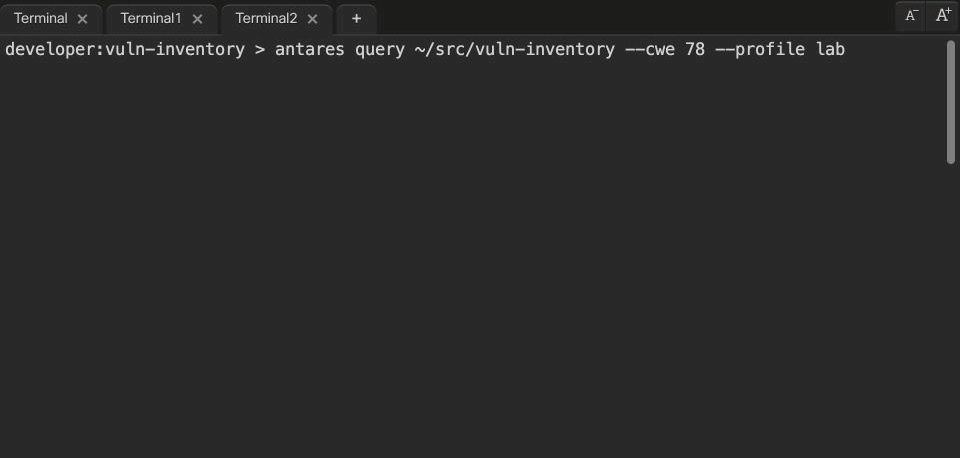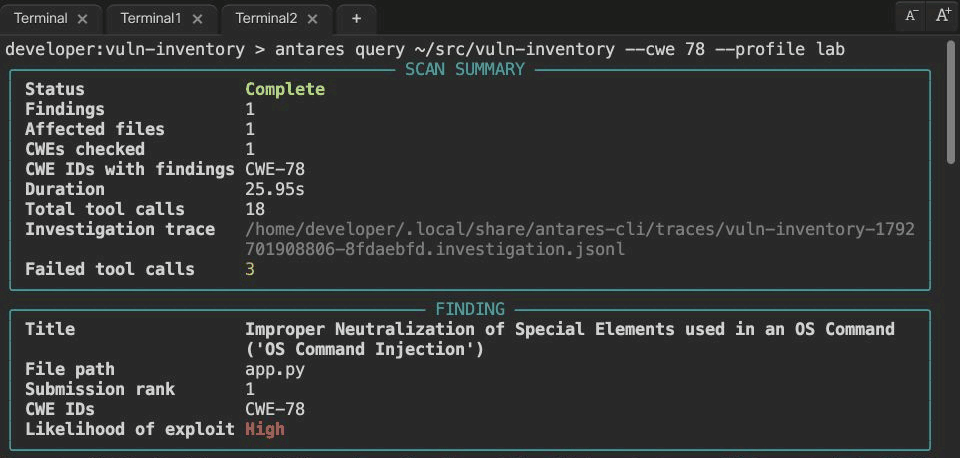
Antares-1B returns app.py as a command-injection candidate for review in the native DevNet GPU lab. This NVIDIA A10G run took 25.95 seconds; playback is condensed to 4.5 seconds. Try this lab
What Antares Does
Finding where a known type of vulnerability actually lives in a large codebase usually means reading it file by file or sending your code to a large cloud model. Antares removes both constraints. It’s a family of compact, open-weight models from Cisco Foundation AI, small enough to run on a single GPU. They do one job: vulnerability localization. You give Antares a weakness type, written as a CWE (a standard category…
