By Guru Baran
Publication Date: 2026-10-09 01:50:00
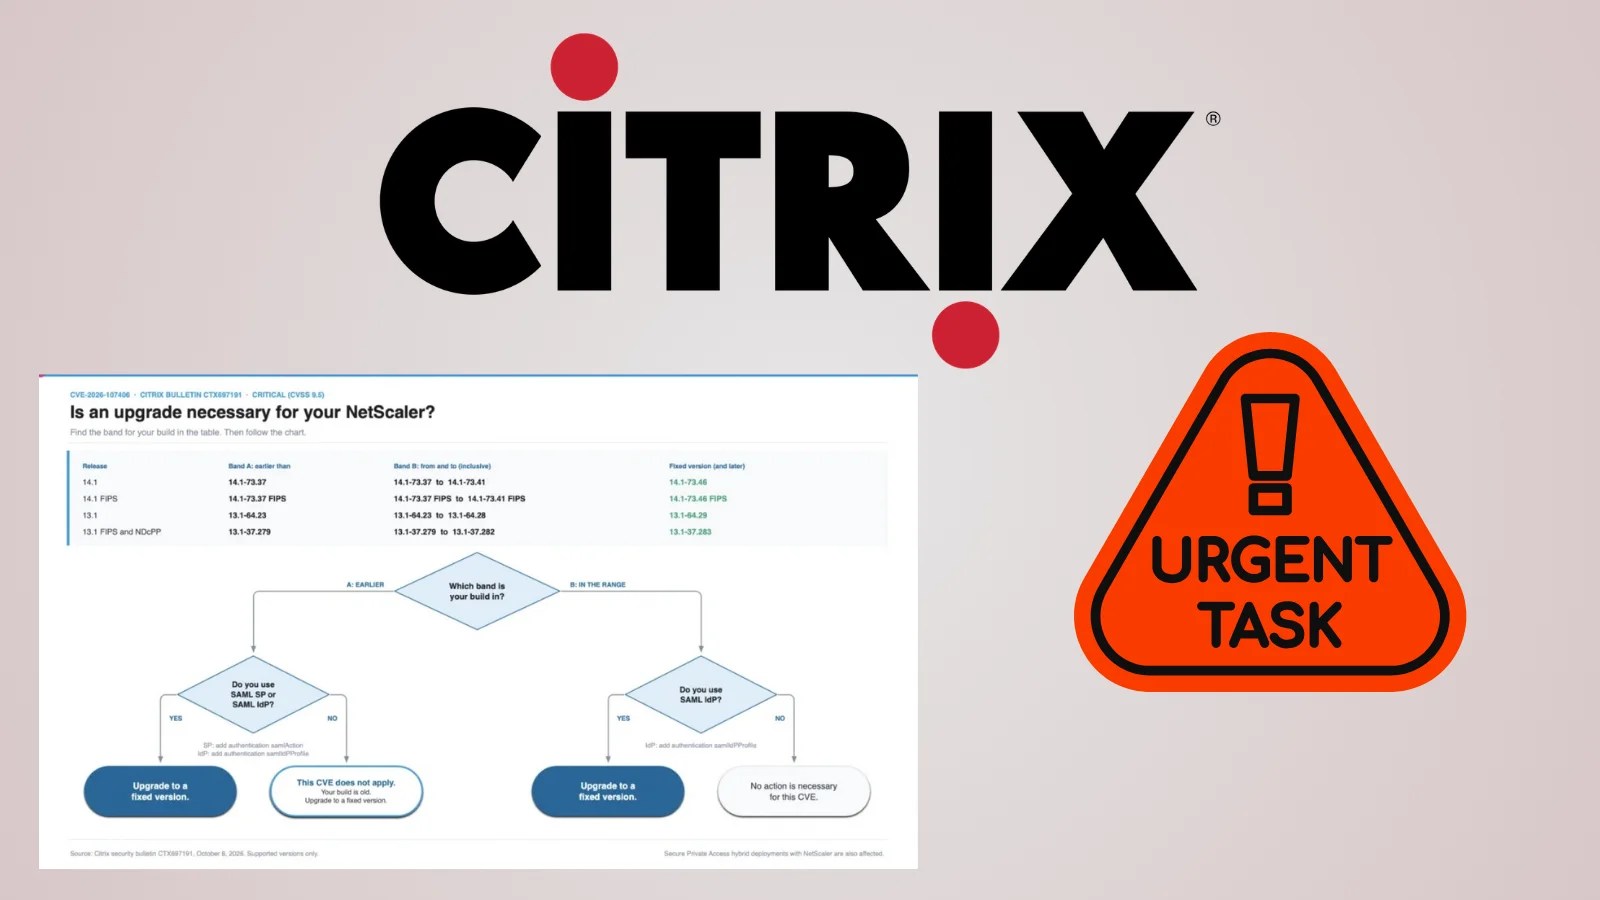
Citrix has urged customers to patch a critical security flaw in NetScaler ADC and NetScaler Gateway that could allow remote code execution or cause a denial of service. Tracked as CVE-2026-107406, the memory overflow vulnerability carries a CVSS v4.0 score of 9.5 and affects appliances with specific SAML settings. The security bulletin, CTX697191, was published on October 8, 2026.
Citrix said it was not aware of any unmitigated exploits when the bulletin was published. That statement should not be read as proof that every deployment is safe. Customers still need to check both their software build and authentication settings to determine whether the flaw applies.
The bulletin classifies the issue as CWE-119, meaning software does not properly restrict operations within a memory buffer. Successful exploitation could let an attacker run code or disrupt service. Its published severity vector describes a network attack requiring no privileges or user interaction, but with high…

