
By Adam Kilgore,
Publication Date: 2026-10-08 15:00:00
We’ve run the Encrypted Visibility Engine (EVE) in Firewall Threat Defense (FTD) at enough conferences to develop a ‘usual suspects’ list of malware detections. Endpoint connections related to Upatre, Xpiro, and Quasar malware are among the most consistent malware related detections in EVE from conference to conference. The Splunk .conf network brought a new detection that we hadn’t seen before: Flawed AMMYY.
AMMYY is a remote access tool that is often misused in scams to gain access to victim computers. There is also a Remote Access Tool (RAT) called Flawed AMMYY that was developed from leaked AMMYY source code, and is directly used as malware. See the MITRE advisory here.
One of the key value propositions of EVE is that it can use granular session fingerprinting to differentiate between similar but distinct applications like AMMYY and Flawed AMMYY. Let’s dig into the events we saw for Flawed AMMYY and some of the details that EVE had to look at.
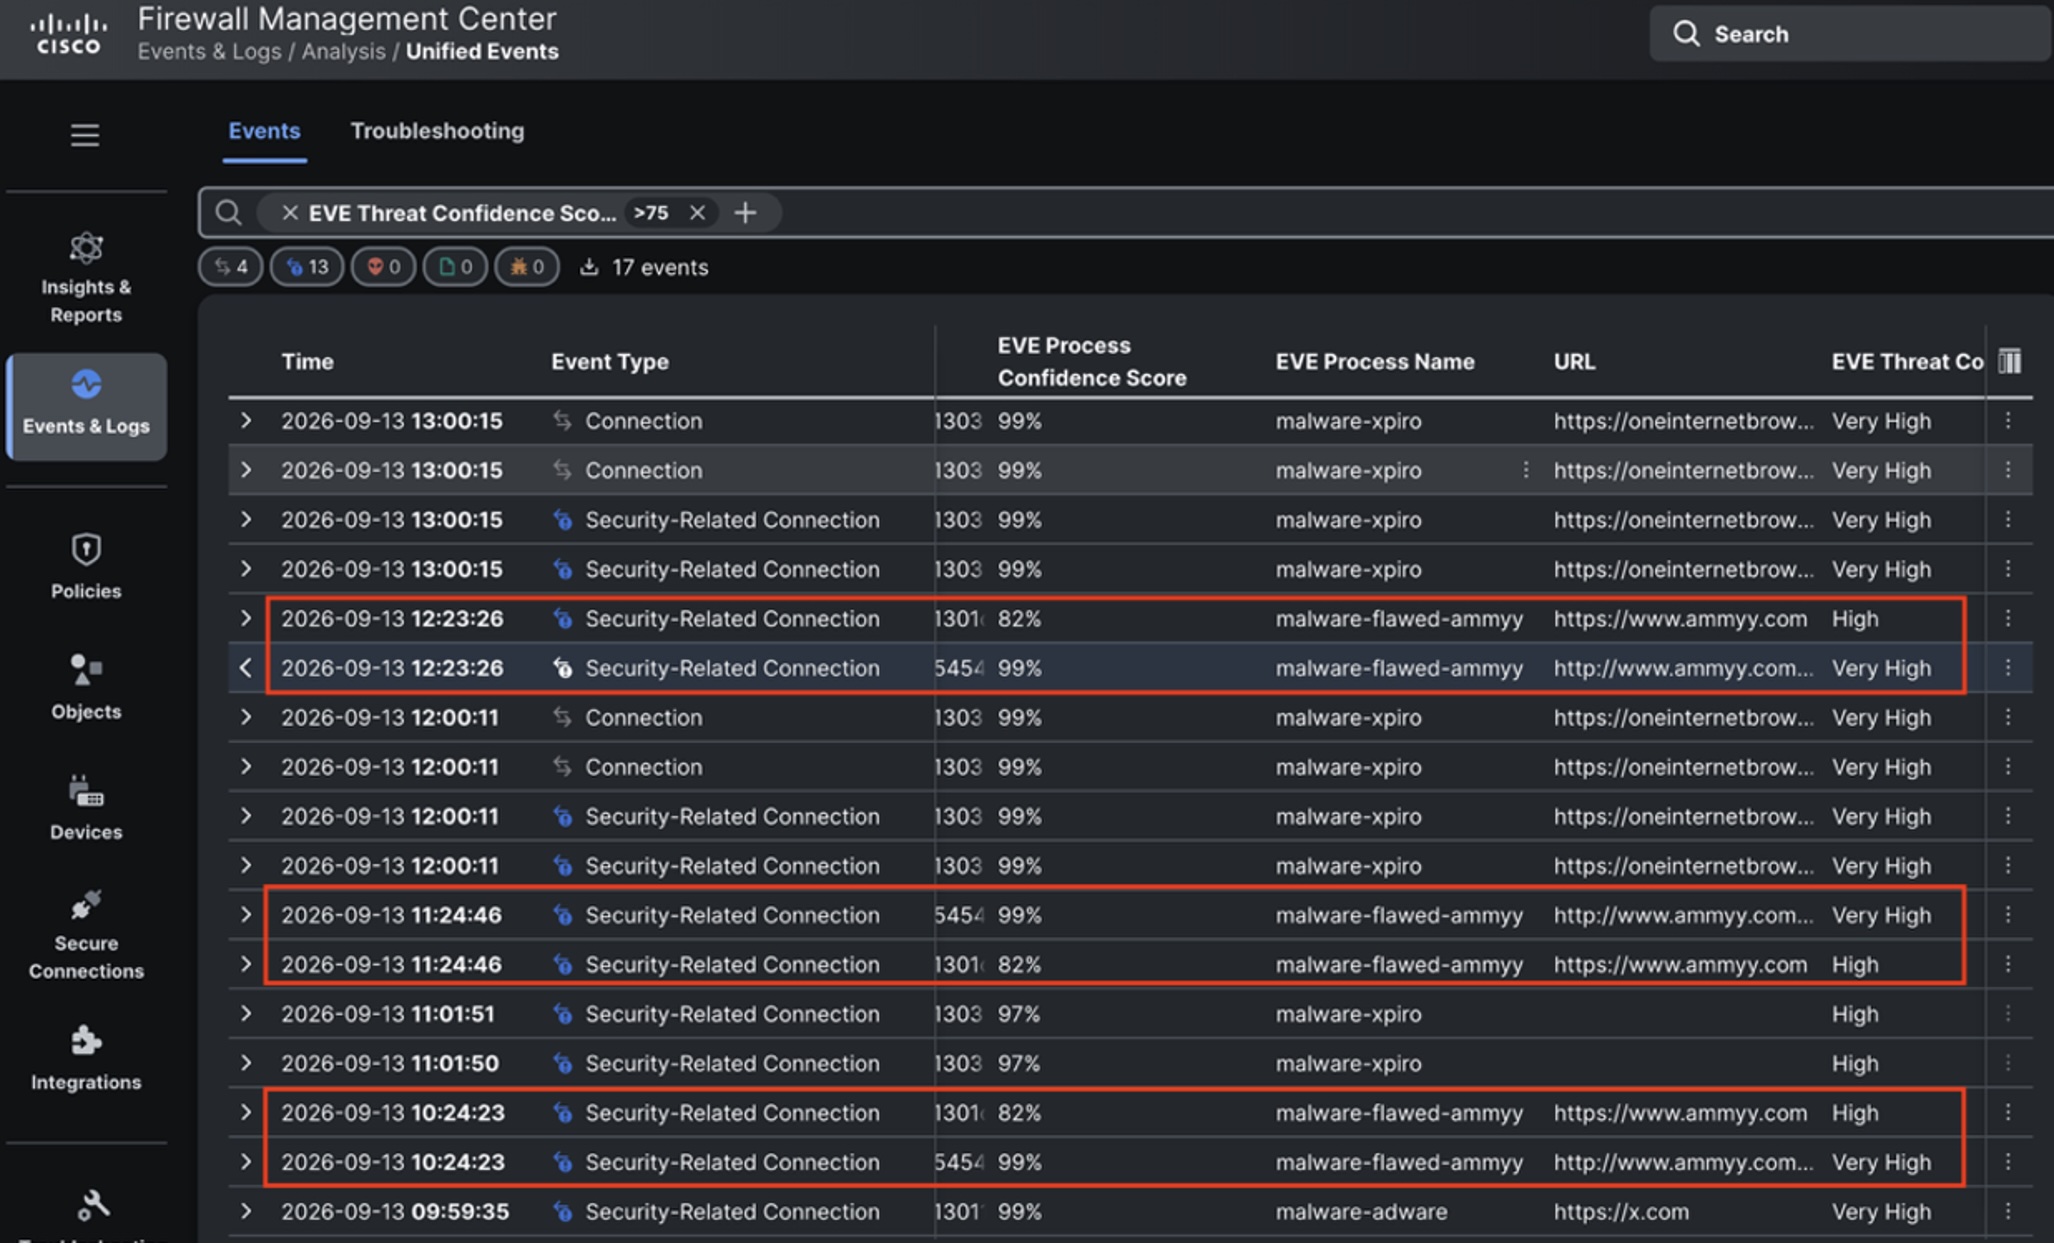
Our EVE detections for…


